
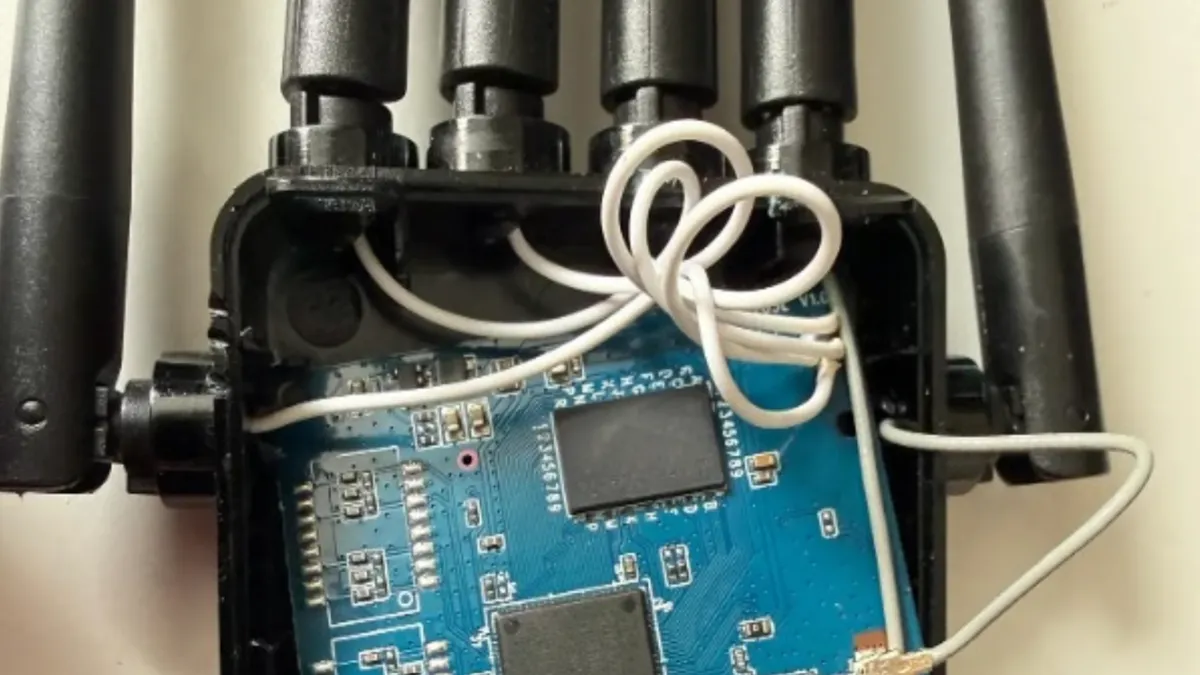
A Wi-Fi extender bought for simply £3 (roughly $3.80 USD) from the web market Temu has been discovered to harbor important safety vulnerabilities, undermining the attraction of ultra-low-cost related gadgets. Safety researcher Keiran Smith’s investigation revealed hidden administrative entry and a universally shared, unchangeable password throughout all items of the system, posing a substantial danger to unsuspecting customers.
Hidden Administrator Entry and Common Password
Smith, who possesses a penetration-testing certification, acquired the six-antenna Wi-Fi extender after encountering an commercial for it on Temu. His examination started by figuring out the system’s inside {hardware}, noting the presence of a MediaTek MT7620 processor, a typical element in finances networking gear. Upon extracting and analyzing the system’s firmware, Smith uncovered a clandestine administrator account that possessed full management over the extender’s capabilities.
Crucially, this hidden account was protected by a set password embedded straight into the system’s software program. This meant that each single extender produced with the identical firmware shared this equivalent, hid administrative credential. Much more regarding, trying to vary the publicly seen administrator password via the system’s commonplace settings interface had no impact on this separate, hidden backdoor account.
Severity of the Hardcoded Password
Smith emphasised the gravity of this specific safety lapse. “It’s value being exact about what makes this as dangerous as it’s, as a result of ‘hardcoded password’ covers a variety of sins,” he acknowledged. He elaborated that this case was extra extreme than typical cases of default passwords as a result of the password was not solely fastened however equivalent throughout all gadgets.
“A default credential is one thing the proprietor can see, is instructed about and might change,” Smith defined. “What we now have right here is the other on each rely.” He additional clarified that the password was a “compile-time fixed,” which means it was hardcoded in the course of the software program’s improvement and remained the identical on each unit offered, somewhat than being derived from distinctive identifiers like a MAC tackle or serial quantity.
Distant Entry and Persistence Considerations
Including to the safety dangers, Smith found that the extender featured a distant login service that may settle for these hidden credentials with out requiring any bodily proximity to the system. This mix of undisclosed administrative entry, a universally shared and unchangeable password, and the potential for distant exploitation creates a considerable safety risk for common customers.
Moreover, Smith discovered that even when a technically adept person managed to find and make the most of this hidden account, any adjustments made may very well be reverted upon restarting the extender. This lack of persistent management over the hidden account provides one other layer of complexity and potential vulnerability.
Broader Implications for Low cost Linked {Hardware}
Past the hardcoded password situation, the researcher’s investigation uncovered further safety weaknesses. A command injection vulnerability was recognized, which might doubtlessly enable malicious actors to execute unauthorized instructions on the system. The extender additionally demonstrated inadequate safety measures surrounding its software program replace course of, doubtlessly creating an avenue for attackers to put in tampered firmware.
Smith acknowledged that these flaws don’t essentially point out intentional malicious design by the producers. It’s believable that these vulnerabilities originated from manufacturing unit testing procedures and have been inadvertently left energetic earlier than the gadgets reached customers. However, the findings spotlight the inherent safety challenges related to extraordinarily cheap good gadgets.
Shopper Consciousness and Future Considerations
This Temu Wi-Fi extender serves as a stark instance of how the pursuit of serious value financial savings on related {hardware} can result in neglected safety implications that reach far past the preliminary buy worth. Shoppers are sometimes drawn to the instant monetary profit, with restricted visibility into the advanced software program selections and safety protocols embedded inside networked gear.
Whereas these particular vulnerabilities don’t indicate that each one budget-friendly networking gadgets are compromised, they underscore the vital significance of fundamental safety diligence. As households more and more combine extra related merchandise into their day by day lives, the potential for hidden software program options to pose dangers to each customers and producers is prone to develop.
The findings recommend a necessity for higher scrutiny of low-cost good gadgets, encouraging producers to prioritize safety all through the event lifecycle and for customers to train warning and search data relating to the safety posture of the related merchandise they buy.
